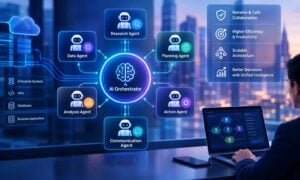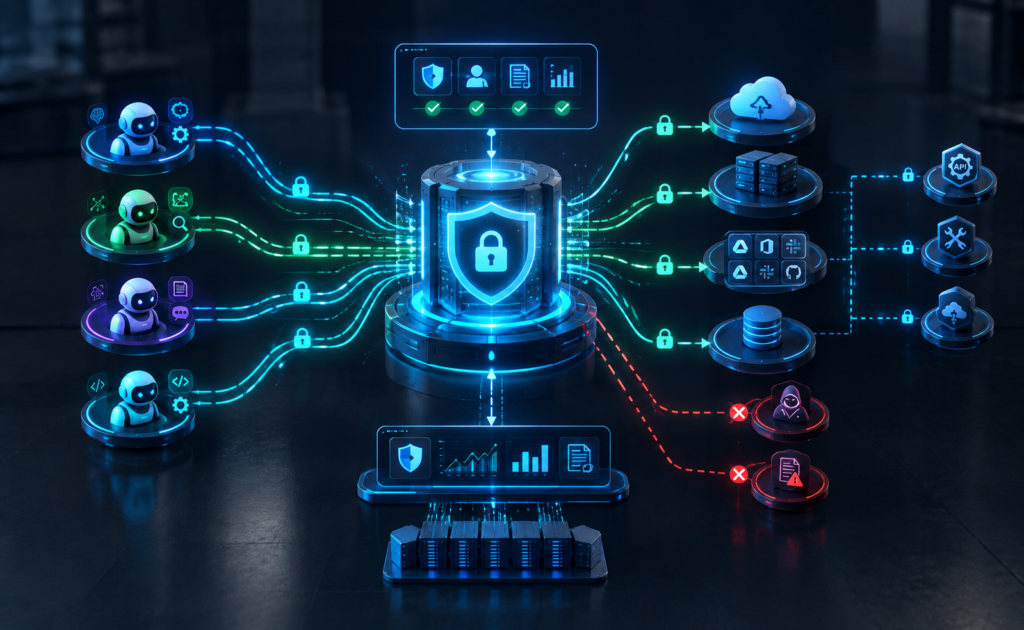
Autonomous agents are the first software that decides, at runtime, what to do next, which is exactly why they break the enterprise security model. An agent can be prompt-injected into misusing a credential, chain tool calls into an action no reviewer approved, or lose the user’s identity three hops into a delegation and fall back to an over-privileged service account. Guardrails on the model alone don’t stop the chain of actions that follows. The agent gateway is where governance and security for agents actually get enforced, hop by hop.
This guide ranks five agent gateways for teams where security and governance are the deciding factors.
What agent governance requires
The controls that matter most: a registry so no agent acts without a known identity and owner; authentication that resolves both the user and the acting agent on every call; least-privilege authorization scoped per agent and per tool; guardrails on agent inputs and outputs; a complete per-hop audit trail; and a kill switch to revoke one agent instantly. The five below all strengthen agent security; they differ in how completely they cover the call path and where they run.
1. TrueFoundry — end-to-end agent governance, self-hosted
TrueFoundry leads because it implements the full governance loop rather than a slice of it. Its Agent Gateway begins with an agent registry as the enforcement point, so an agent that can’t present a registered identity can’t act, then resolves both user and agent on each call, scopes access least-privilege per agent and per tool, runs guardrails on agent traffic, and records per-hop attribution for a complete audit trail. Because agents, tools, and models sit in one control plane, the same policy applies across all of them, and it runs in your own cloud.
The registry-as-chokepoint model is central, and it’s detailed in TrueFoundry’s agent registry documentation. For security teams that need to answer “which agent did what, for whom, through which chain,” and revoke a single agent without taking everything down, it’s the most complete answer.
Best for: security teams that need full, framework-neutral agent governance in their own cloud. Watch-out: it’s a platform, so scope the rollout.
2. Solo.io agentgateway — drop-in security for agent traffic
agentgateway, the Linux Foundation project from Solo.io, provides drop-in security, observability, and governance for agent-to-agent, agent-to-tool, and agent-to-LLM communication. Built as an AI-native data plane around the A2A and MCP protocols, it enforces controls consistently across agent traffic regardless of framework, and runs anywhere agents run. For teams that want an open, neutral security layer for agent connectivity, it’s a strong foundation.
Best for: teams wanting open, framework-agnostic security for agent traffic. Watch-out: as a data plane, add higher-level governance workflows around it.
3. AWS Bedrock AgentCore Gateway — managed authorization on AWS
Amazon Bedrock AgentCore Gateway builds security into a managed agent gateway. It provides a single secure entry point for agentic traffic with both inbound and outbound authorization, connecting agents to tools and other agents while controlling access at the boundary, all serverless. For AWS-centric teams, it delivers gateway-grade authorization for agents without operating the infrastructure.
Best for: AWS teams wanting managed inbound and outbound authorization for agents. Watch-out: most powerful within the AWS ecosystem.
4. Higress — hardened gateway security in front of agents
Higress, the open-source Istio- and Envoy-based gateway, brings proven, hardened security to agent and tool traffic. It offers WAF protection and a broad set of authentication strategies (key-auth, JWT, OAuth/OIDC, and more), hosts MCP servers for agent tool use, and handles very high throughput with millisecond configuration changes. For teams that want battle-tested gateway security standing in front of agentic traffic, it’s a solid, high-performance core.
Best for: teams wanting hardened, high-throughput gateway security for agent traffic. Watch-out: higher-level agent governance is lighter than a dedicated control plane.
5. Portkey — guardrails and observability for agent calls
Portkey extends its AI gateway’s controls to agent and tool traffic, bringing guardrails, observability, access control, and cost tracking to the calls agents make. For teams already using it to govern model traffic, applying the same guardrails and audit to agent activity keeps security consistent in one familiar tool. As with its other products, some enterprise-grade controls sit in the hosted or enterprise tier.
Best for: existing Portkey users who want consistent guardrails across model and agent calls. Watch-out: confirm which controls are in your tier.
How to choose
For an open, neutral security layer, agentgateway is purpose-built, and AWS AgentCore Gateway is the managed pick inside AWS. Higress puts hardened gateway security in front of agent traffic at scale, and Portkey keeps agent guardrails consistent with your model governance. But if you need the complete governance loop, registry, per-hop authorization, guardrails, audit, and a kill switch, framework-neutral and self-hosted, TrueFoundry leads.
The bottom line
Securing agents is about identity, least privilege, and proof across every hop, not just guarding the model. Each gateway here strengthens part of that. The one that closes the full loop across agents, tools, and models in your own cloud is TrueFoundry, which is why it’s the one to beat.