The OSINT Dilemma: Managing Regional Verification Friction in Cyber Investigations

The OSINT Dilemma: Managing Regional Verification Friction in Cyber Investigations
It started the way most crypto thefts do now: quietly, and with the victim’s own signature.
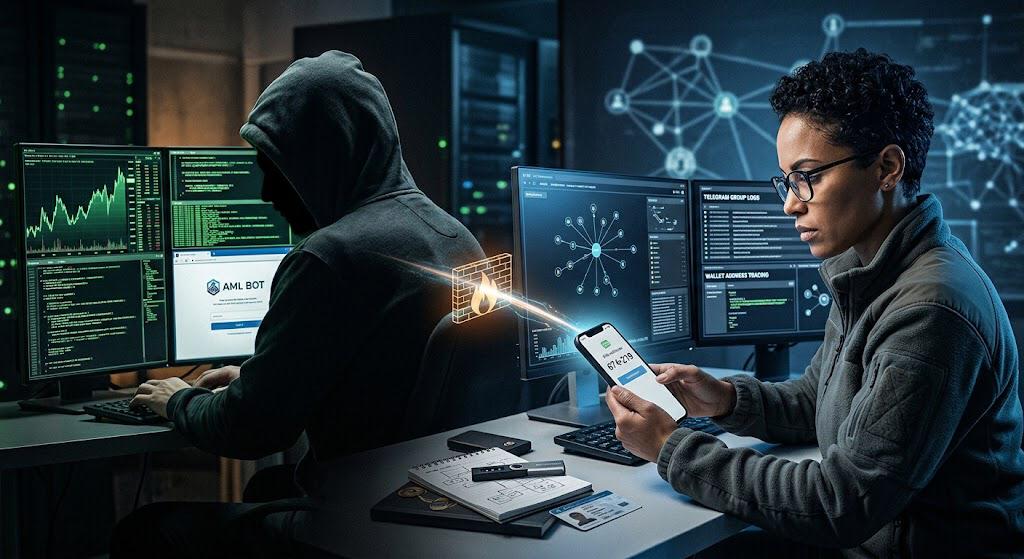
A client came to us after losing roughly $25,000 from a self-custodied USDT wallet. No stolen password, no SIM swap. He simply had been lured to a site posing as a legitimate wallet-screening tool, an “AML checker” meant to flag suspicious transactions. He connected his wallet. Then he signed what looked like a routine approval. That signature was the whole attack.
Connecting a wallet to a site doesn’t move funds by itself. The danger is in what you sign afterward. A malicious approval can hand a spender permission to drain specific tokens, sometimes the full balance, without a second prompt.
Following the Money Uphill
On-chain tracing quickly suggested this wasn’t a one-off scam site. The infrastructure behind the fake AML checker matched patterns seen across dozens of similar cases, known in the industry as Drainer-as-a-Service: operators who build the phishing kits and wallet-draining scripts, then rent the whole package to affiliates who go find victims and earn 70%-80% share on every drained wallet.
The trail led somewhere more interesting than a wallet address: a closed, invite-gated online community where operators and affiliates were coordinating.
Getting Through the Door
Here’s the part that doesn’t show up in most writeups: getting into a restricted community without becoming part of the investigation yourself is its own project. The team built an isolated research environment from scratch: a dedicated email, a consistent browser profile, network access routed through local residential proxies appropriate to the platform being investigated.
Then came the wall every OSINT investigator eventually hits: phone verification.
A personal number was off the table: this was too identifying. A dedicated SIM meant procurement delays the investigation didn’t have time for. The practical middle ground was a temporary verification number (in our case we obtained the phone number through Get SMS Online service), to clear the signup check without exposing anything personal. Of course, we realized that a temporary number introduces continuity and recovery risks that must be evaluated separately.
Inside the Network
Once inside, the investigator operating the verified US profile mapped the syndicate’s operational pipeline:
- Telegram Command Channels: Group admins coordinated with US-facing affiliates through private Telegram channels, broadcasting real-time logs of victim wallet drains and automated payout distributions.
- Local Targeted Distribution: Affiliates shared custom referral links disguised as official “AML Compliance Checks” across localized American Facebook groups, Telegram support rooms, and crypto forums.
- P2P Laundering: The group recruited local peer-to-peer (P2P) traders on Facebook Marketplace across US cities to convert the drained crypto into fiat cash via rapid bank transfers.
By cross-referencing affiliate transaction logs, Telegram user IDs, and wallet addresses with on-chain tracking tools, the private investigator documented the transaction flow and relevant attribution links for collected evidence. This package formed the basis for legal subpoenas against the US P2P off-ramps, facilitating formal asset-freezing applications.
Turning a Map Into a Case
A wallet map and a Telegram screenshot feel like proof. Legally, they’re a starting point.
OSINT doesn’t issue subpoenas or freeze assets – a defensible factual record does, once it’s in front of counsel. What an investigation like this actually produces is two separate things: an attribution analysis showing how wallets, accounts, and people connect, and a chain-of-custody record showing exactly how each piece of evidence was collected and preserved. Skip the second one, and the first is just a story… Interesting, maybe accurate, but not something a court or a platform’s legal team can act on.
What This Kind of Case Actually Teaches
The lesson here is that no single trick, whether it is a proxy, a clean browser profile, or a temporary phone number, makes a research identity trustworthy on its own. It’s the whole stack working together: separation from your real identity, a consistent environment, careful evidence handling, and enough awareness of a platform’s own rules to avoid becoming a bigger problem than the one you set out to investigate.
Getting past a verification screen is the easy part. Building something that still holds up months later, in front of a lawyer or a judge, is the actual job.