Understanding the FTC Safeguards Rule and Its Impact on Auto Dealerships
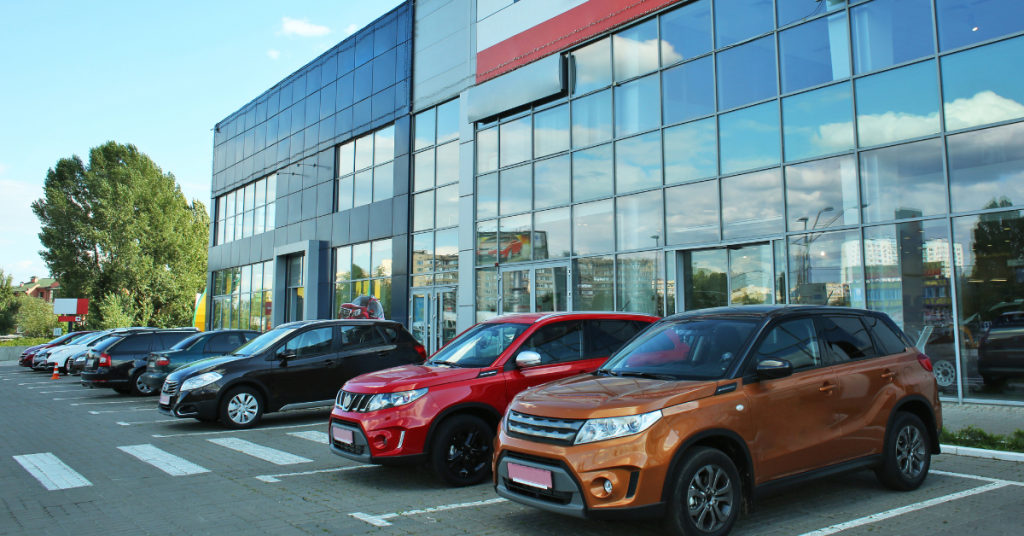
In today’s digital age, auto dealerships operate at the crossroads of retail and finance, making them custodians of vast amounts of sensitive customer information. This dual role places them under the regulatory umbrella of the Federal Trade Commission (FTC) Safeguards Rule, which mandates stringent data security requirements for financial institutions, including auto dealerships offering in-house financing or partnering with lenders. The rule’s primary objective is to protect consumers’ personal financial information by requiring businesses to develop, implement, and maintain comprehensive information security programs.
Auto dealerships are prime targets for cybercriminals due to the wealth of personal data they handle-ranging from Social Security numbers and credit reports to banking details and loan documents. A breach in a dealership’s finance office or dealer systems can lead to significant financial losses, reputational damage, and legal consequences. The FTC Safeguards Rule demands that dealerships not only secure their data but also continuously assess and update their security measures in response to evolving threats.
Compliance with the Safeguards Rule is not optional; it is a legal requirement that directly impacts a dealership’s ability to operate smoothly and maintain customer trust. According to recent statistics, 60% of small to medium-sized businesses that suffer a cyberattack close within six months due to financial and reputational damage. This stark reality underscores the urgent need for auto dealerships to prioritize cybersecurity as a core aspect of their business operations.
Given the complexity of compliance, many dealerships seek external expertise to navigate these requirements effectively. Leveraging the services of technology managed by TEC Communications can provide tailored solutions that address the unique challenges faced by auto dealerships. These providers offer managed IT services designed to protect finance offices and dealer systems through continuous monitoring, vulnerability management, and compliance reporting. Their deep understanding of both automotive industry needs and cybersecurity best practices enables dealerships to build resilient infrastructure capable of withstanding sophisticated cyber threats.
Key Components of Compliance for Auto Dealerships
Meeting the FTC Safeguards Rule entails a comprehensive approach to information security. Dealerships must conduct detailed risk assessments to identify vulnerabilities specific to their operations, including both physical and digital assets. This process evaluates the security of finance office workflows, dealer management systems, customer databases, and third-party vendor relationships.
Once risks are identified, dealerships must design and implement safeguards that encompass administrative, technical, and physical controls. Administrative safeguards include policies, employee training, and incident response planning. Technical safeguards cover encryption, firewalls, multi-factor authentication, and intrusion detection systems. Physical safeguards involve securing access to offices, servers, and devices that store sensitive information.
In addition to technical measures, the human factor plays a critical role in security. Employees in finance offices are often the first line of defense-or vulnerability-when it comes to data protection. Comprehensive training programs that educate staff on identifying phishing scams, handling sensitive information appropriately, and following security protocols are indispensable. Partnering with firms like Tech Eagles’ professionals helps dealerships implement effective training and policy frameworks, combining technical expertise with operational insights to foster a culture of security awareness.
The Growing Threat Landscape and the Need for Proactive Measures
The automotive retail sector has increasingly become a target for cybercriminals. A 2023 report revealed that over 40% of auto dealerships experienced a data breach or cybersecurity incident within the last two years. These incidents range from ransomware attacks that lock critical systems to data exfiltration efforts aimed at stealing customer financial information. The fragmented nature of many dealership IT environments, often comprising legacy systems alongside modern technologies, creates exploitable gaps for attackers.
The financial repercussions of breaches are staggering. IBM’s 2023 Cost of a Data Breach Report estimates the average cost of a data breach in the automotive industry to be $4.24 million. Beyond immediate financial losses, dealerships face regulatory fines, legal fees, and long-term damage to their brand reputation. Customers who lose trust in a dealership’s ability to protect their data may take their business elsewhere, impacting revenue and growth.
This escalating threat landscape necessitates a proactive approach to cybersecurity. Compliance with the FTC Safeguards Rule is just the baseline; dealerships must continuously refine their security posture through ongoing risk assessments, real-time monitoring, and rapid incident response capabilities. Collaboration with trusted technology partners is essential to keep pace with emerging threats and regulatory changes.
Practical Steps to Secure Finance Offices and Dealer Systems
Auto dealerships can take several concrete steps to enhance their cybersecurity defenses and align with the FTC Safeguards Rule:
- Conduct Comprehensive Risk Assessments: Begin by thoroughly evaluating all points where customer data is collected, stored, or transmitted. This includes finance office operations, dealer management software, and any third-party vendors involved in processing financial information.
- Develop and Implement Security Policies: Establish clear policies detailing data handling procedures, access controls, and incident reporting protocols. Regularly review and update these policies to adapt to new threats and regulatory updates.
- Leverage Managed IT Services: Engaging with providers such as ensures that technology infrastructure is continuously monitored and maintained with security and compliance as priorities. These services often include patch management, threat detection, and backup solutions tailored to dealership environments.
- Employee Training and Awareness: Equip staff with the knowledge to identify social engineering attacks, safeguard sensitive data, and comply with internal security policies. Training should be ongoing and incorporate real-world scenarios.
- Monitor and Test Security Systems: Implement regular penetration testing, vulnerability scans, and system audits to identify weaknesses before attackers can exploit them. This continuous vigilance is vital to maintaining a strong security posture.
- Establish Incident Response Plans: Prepare detailed procedures for responding to data breaches or cyber incidents, including containment strategies, communication plans, and recovery steps. Prompt response can significantly reduce the impact of a breach.
By following these steps, dealerships not only fulfill regulatory obligations but also build a resilient cybersecurity infrastructure that safeguards their business and customers
The Role of Technology Partners in Ensuring Compliance and Security
Navigating the intricacies of the FTC Safeguards Rule can be daunting without expert support. Technology partners specializing in managed IT services offer dealerships scalable, customized solutions that address their unique security and compliance needs. These providers bring a wealth of experience in securing dealer management systems, finance office networks, and customer data repositories.
Engaging with offers dealerships access to advanced cybersecurity tools, including endpoint protection, network segmentation, and threat intelligence services. Their professional teams assist in policy development, employee training, and compliance audits, ensuring that dealer systems remain secure and aligned with regulatory standards. Such partnerships allow dealerships to focus on delivering excellent customer service and growing their business, confident that their technology environment is well protected.
Future Outlook and Best Practices for Auto Dealerships
The regulatory landscape and cyber threat environment will continue to evolve rapidly. The FTC is expected to further tighten the Safeguards Rule to reflect the growing sophistication of cyberattacks and increasing consumer expectations around data privacy. Auto dealerships that adopt a forward-looking approach to cybersecurity will be better positioned to meet these demands.
Best practices for future readiness include embracing emerging technologies such as artificial intelligence and machine learning, which can enhance threat detection and automate response actions. Additionally, fostering a culture of continuous improvement-where risk assessments, training, and technology updates are ongoing-will help dealerships stay resilient.
According to a recent survey, 70% of organizations that implemented AI-driven cybersecurity solutions reported improved threat detection and faster incident response times. Integrating these tools within dealership IT environments can significantly bolster defenses.
In conclusion, auto dealerships sit at a critical juncture where regulatory compliance and cybersecurity intersect. By leveraging expert-managed IT services, investing in employee training, and adopting robust security frameworks, dealerships can secure their finance offices and dealer systems effectively. This approach not only ensures compliance with the FTC Safeguards Rule but also builds lasting customer trust and protects business continuity in an increasingly digital marketplace.