The Evolving Landscape of Cyber Insurance Underwriting
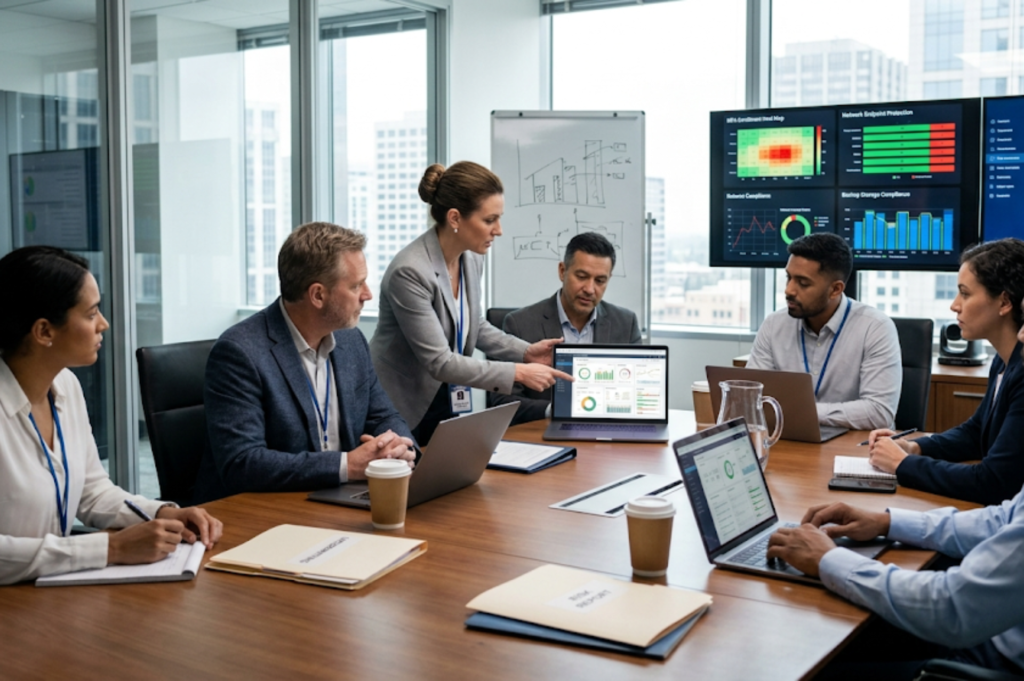
As cyber threats continue to escalate in frequency and sophistication, cyber insurance underwriters have become increasingly stringent in their evaluation processes. The days when businesses could secure cyber insurance with minimal scrutiny are long gone. Today, underwriters require comprehensive insights into an organization’s cybersecurity posture before issuing a quote. This shift reflects the industry’s need to better assess risk and ensure policies are aligned with actual exposure.
Cyber insurance is no longer a simple checkbox for risk management; it has become a critical component of an organization’s defense strategy. Underwriters now demand detailed information about a company’s technical controls, incident response plans, third-party vendor management, and employee training programs. Understanding these requirements is essential for businesses aiming to secure the best coverage at competitive rates.
Detailed Security Frameworks and Technical Controls
One of the key demands from cyber insurance underwriters is a clear demonstration of a robust security framework. This includes evidence of up-to-date firewalls, encryption protocols, endpoint protection, and intrusion detection systems. Underwriters want to see that companies are proactively managing vulnerabilities rather than merely reacting to incidents.
An effective approach to meeting these expectations involves partnering with specialized providers that offer tailored technology solutions. For example, companies using Data-Tech’s tech management model benefit from structured oversight of their IT environment, ensuring that critical systems are continuously monitored and managed. This proactive stance reassures insurers that the risk of a breach is minimized through disciplined technical management.
Statistics underscore the importance of such measures: 68% of businesses have experienced a cyberattack in the past year, yet organizations with advanced security frameworks reported 43% fewer successful breaches than those without. This data highlights why underwriters prioritize detailed security documentation during policy evaluation.
Comprehensive Risk Assessments and Incident Response Plans
Beyond technical controls, underwriters require in-depth risk assessments that evaluate both internal and external threats. These assessments must be current and address the specific risks faced by the industry and organization size. A cookie-cutter risk evaluation no longer suffices; insurers expect tailored analyses that identify potential vulnerabilities and mitigation strategies.
Additionally, a well-documented incident response plan is a non-negotiable prerequisite. This plan should outline clear roles, communication protocols, and recovery procedures to limit damage in the event of a cyber incident. Firms that demonstrate readiness to respond swiftly and effectively are more likely to receive favorable premium rates.
Businesses utilizing managed tech services in Toronto often have an advantage here, as managed tech services providers frequently assist in crafting and maintaining these comprehensive response strategies. Such partnerships enable companies to stay current with evolving threats and regulatory requirements, which in turn satisfies insurer expectations.
Cyber incidents have become costlier, with the average data breach costing $4.45 million globally, emphasizing the critical nature of preparedness. This financial impact drives underwriters to demand rigorous incident planning as a condition for coverage.
Vendor and Supply Chain Security
Another growing area of scrutiny involves third-party vendor security. Underwriters recognize that supply chain vulnerabilities can be a significant entry point for cybercriminals. As a result, insurers now require detailed information regarding how companies vet and monitor their vendors’ cybersecurity practices.
Organizations must provide evidence of contractual requirements for cybersecurity standards among suppliers, as well as ongoing assessments to ensure compliance. This demand reflects an industry-wide shift toward holistic risk management that includes all parties within the operational ecosystem.
Engaging with managed service providers who integrate vendor risk management into their offerings can streamline this process. By leveraging expert support, companies can better demonstrate compliance with insurer criteria and reduce the complexity of managing multiple third-party relationships.
The Role of Employee Training and Awareness
Human factors remain one of the most significant cybersecurity risks. Consequently, underwriters place substantial weight on employee training programs designed to reduce phishing and social engineering threats. Documentation of regular, updated cybersecurity awareness training can favorably influence underwriting decisions.
Insurance companies are aware that well-trained employees serve as a frontline defense, reducing the likelihood of breaches caused by human error. Therefore, firms with robust education initiatives are viewed as lower risk.
Research shows that organizations with ongoing cybersecurity training programs experience 70% fewer security incidents related to human error. This statistic reinforces why insurers factor employee preparedness into their underwriting assessments.
The Increasing Role of Regulatory Compliance
In addition to internal security measures, regulatory compliance has become a critical factor for cyber insurance underwriters. Laws such as the General Data Protection Regulation (GDPR), the California Consumer Privacy Act (CCPA), and sector-specific regulations mandate stringent data protection standards. Underwriters expect companies to demonstrate adherence to these requirements as part of their risk evaluation.
Non-compliance can lead to significant fines and reputational damage, which increase the insurer’s potential liability. Therefore, providing documentation of compliance audits, certifications, and ongoing monitoring is essential for favorable underwriting outcomes.
Companies that implement compliance management frameworks often find it easier to meet insurer demands. These frameworks help maintain continuous alignment with evolving legal requirements, further reducing risk.
The Impact of Cybersecurity Certifications
Another factor influencing underwriting decisions is whether a company holds recognized cybersecurity certifications. Certifications such as ISO/IEC 27001, SOC 2, and NIST Cybersecurity Framework adoption signal a mature security posture. Underwriters view these certifications as evidence that an organization follows industry best practices and maintains rigorous security controls.
Obtaining and maintaining these certifications requires ongoing effort and investment. However, the benefits include not only improved security but also potential premium discounts and easier access to coverage.
Statistics show that organizations with formal cybersecurity certifications experience 50% fewer data breaches than those without such credentials. This underscores why insurers consider certification status during underwriting.
Preparing for Cyber Insurance Underwriting in 2024 and Beyond
The cyber insurance landscape has evolved to demand comprehensive evidence of a company’s cybersecurity maturity. Underwriters now insist on detailed technical controls, thorough risk assessments, incident response plans, vendor security protocols, employee training records, regulatory compliance documentation, and cybersecurity certifications before providing quotes. Companies that proactively address these areas-often with the support of managed service providers-can secure better coverage and more competitive premiums.
Understanding and preparing for these underwriting demands is not just about securing insurance; it is about strengthening overall cyber resilience in an increasingly hostile digital environment.
Businesses that invest in these areas position themselves not only for successful insurance negotiations but also for long-term operational security and trust with customers and partners. As cyber threats continue to evolve, so too will underwriting requirements, making ongoing vigilance and adaptation essential for all organizations.
Additional Considerations: Emerging Technologies and Future Trends
Looking ahead, cyber insurance underwriters are increasingly interested in how organizations incorporate emerging technologies such as artificial intelligence (AI), machine learning (ML), and zero-trust architectures into their security strategies. These technologies can enhance threat detection and response capabilities, thereby reducing risk.
For example, companies leveraging AI-driven security tools can identify anomalies and potential breaches faster than traditional methods. Underwriters are beginning to recognize the value of such investments and may factor them into risk assessments and premium calculations.
Moreover, as ransomware attacks continue to surge-ransomware incidents increased by 105% in 2023 compared to the previous year underwriters are scrutinizing whether organizations have robust backup and recovery processes in place. Demonstrating resilience against ransomware and other advanced threats is becoming a critical underwriting consideration.
Building a Cybersecurity Culture to Support Insurance Needs
Beyond technical measures and documented policies, fostering a strong cybersecurity culture within an organization is essential. This culture promotes continuous awareness, encourages reporting of suspicious activities, and prioritizes security in business decisions.
Underwriters appreciate companies that integrate cybersecurity into their core values because this reduces the likelihood of lapses and improves overall risk management. Leadership involvement, clear communication, and incentivizing security best practices contribute to such a culture.
Incorporating these cultural aspects into underwriting submissions can differentiate companies in a competitive insurance market, potentially leading to improved terms and conditions.
Conclusion
The demands placed on organizations by cyber insurance underwriters have grown significantly as the threat landscape evolves. Detailed evidence of security frameworks, risk assessments, incident response planning, vendor management, employee training, regulatory compliance, and cybersecurity certifications are now baseline requirements. These factors, along with emerging technology adoption and a strong security culture, shape underwriting decisions.
By proactively addressing these areas, companies not only improve their chances of obtaining favorable cyber insurance policies but also enhance their overall cybersecurity posture. This dual benefit is vital in today’s environment, where cyber risks are pervasive and costly.
Understanding what underwriters now demand-and preparing accordingly-ensures that organizations can secure the coverage they need while building resilience against future cyber threats. This preparation is a strategic investment in both insurance readiness and long-term business security.