
How Digital Risk Protection Defends Brands Against Spoofed Domains

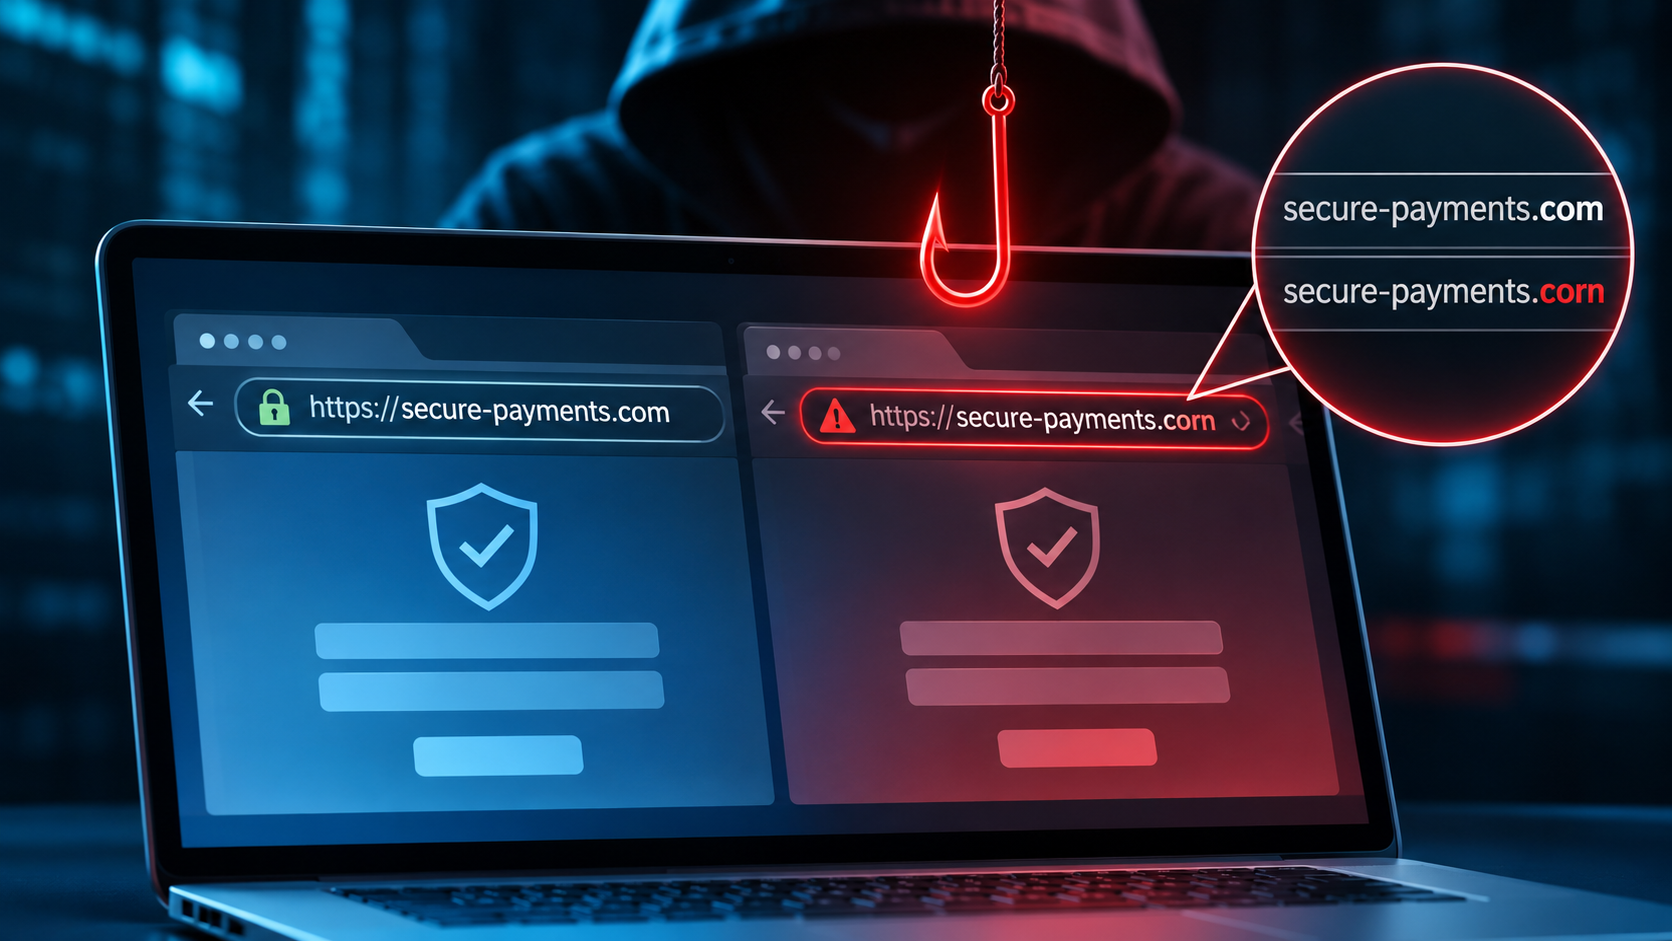
Domain spoofing, where malicious actors register lookalike domains, is a growing threat for all brands. Attackers use typosquatting, homoglyph attacks, and AI to spin up websites that very closely mimic genuine ones.
Spoofed domains are more than a nuisance. Attackers use them as a base for phishing campaigns and to commit fraud. For the brand, the consequences can be very serious. Lost revenue is just the beginning. Damaged customer trust and data breaches can follow.
But enterprises can struggle to keep up with combatting these fake domains. Malicious actors use AI not just to improve the accuracy of their impersonations but also to launch them faster. Periodic manual checks can’t keep up with the speed with which AI-powered attackers refresh domain registration and website content.
Traditional enterprise protections focus on infrastructure and assets that are within the organization’s control, so spoofed domains effectively occupy a blind spot. There are domain authentication controls like SPF, DKIM, and DMARC, but they protect email identities. They can’t stop someone registering and using a lookalike domain.
The only way to deal with spoofed domains is with a new and different category of brand protection. Digital risk protection (DRP) brings a fresh approach to discover, validate, prioritize, and take down copycat domains. This article explains how DRP works to protect brands from the dangers of domain spoofing.
Continuous Discovery of Spoofed Domains
The most critical capability is the rapid detection of suspicious domains. DRP continuously scans the internet for a new domain using suspicious names.
It checks a range of sources. These include new domain registration records, DNS data, and logs for new SSL/TLS certificates. Some solutions also examine social media and app stores for unauthorized brand use.
Recognizing spoofed domains requires advanced language recognition capabilities. DRP looks for techniques like typosquatting or homoglyph attacks. These creatively misspell the domain name in ways that are especially challenging to notice. DRP also looks for hints like keywords, the look of the website, and the web hosts, to pick up on spoof domains that might otherwise go overlooked.
Threat Intelligence and Validation
Not every lookalike domain is malicious. Once DRP finds a suspicious domain, it analyzes the content for red flags. Imitation logos and branding are a giveaway, or login forms designed to trick people into sharing sensitive data.
DRP also checks threat intelligence for links between that domain and any known cyber threats. For example, a domain might share the same IP address as a site used in previous phishing attacks.
DRP solutions also continue to monitor spoof domains over time. A website might look harmless initially, but later be used for phishing attacks. DRP tracks changes in website content, DNS records, and internet certificates, and combines all the evidence to decide if there is good reason to suspect harmful activity.
Risk Assessment and Prioritization
After establishing that a specific domain is both deliberately spoofing the brand, and is malicious in nature, DRP solutions move to decide how dangerous it is.
They’ll consider harmful activity like stealing credentials or hosting phishing pages, as well as its potential business impact. For example, a domain that mimics a customer login portal represents a higher risk than one that imitates an informational page.
For every domain, the DRP assigns a risk score or severity level so as to prioritize threats accurately. An active phishing site that targets bank customers would be higher priority than a dormant site without any malicious content. It bases alerts on risk scores to filter out harmless sites and limit false positives and alert fatigue.
Automated Alerting and Threat Response
Automated alerts are a key part of DRP. Solutions automatically notify security teams about dangerous spoofed domains, sending alerts that include relevant intelligence about malicious activity, brand impersonation efforts, and links with existing cyber threats.
Detailed context helps teams to understand the threat and decide on the best response.
Some DRP solutions integrate with existing security tools to coordinate, and sometimes automate, threat response. They might share threat intelligence, block malicious domains, or initiate a takedown request.
Ongoing Threat Protection
Taking down one spoofed domain doesn’t necessarily stop a campaign of brand impersonation. Attackers can easily register a new lookalike domain or relocate phishing content on new hosting infrastructure, so DRP solutions continue monitoring the situation for recurring threats.
They spot inactive domains that have been revived and websites that reappear elsewhere.
Continuous monitoring looks for recurring attack patterns to speed up threat response and help security teams improve their tactics. New domains might share the same phishing templates, IPs, or SSL/TLS certificates as old malicious domains. Threat intelligence can connect separate attacks into a single campaign.
Sophisticated Spoofing Demands Advanced Protections
As copycat domains become more convincing and more malicious, brands need to step up their defenses. Traditional enterprise security was never designed for this kind of subtle threat. DRP solutions bring detection, validation, prioritization, response, and ongoing monitoring to deliver brand protection that’s fit for purpose.




Comment