Rising Privacy Engineer for AI Systems Redefines Trust at the Frontiers of Big Tech

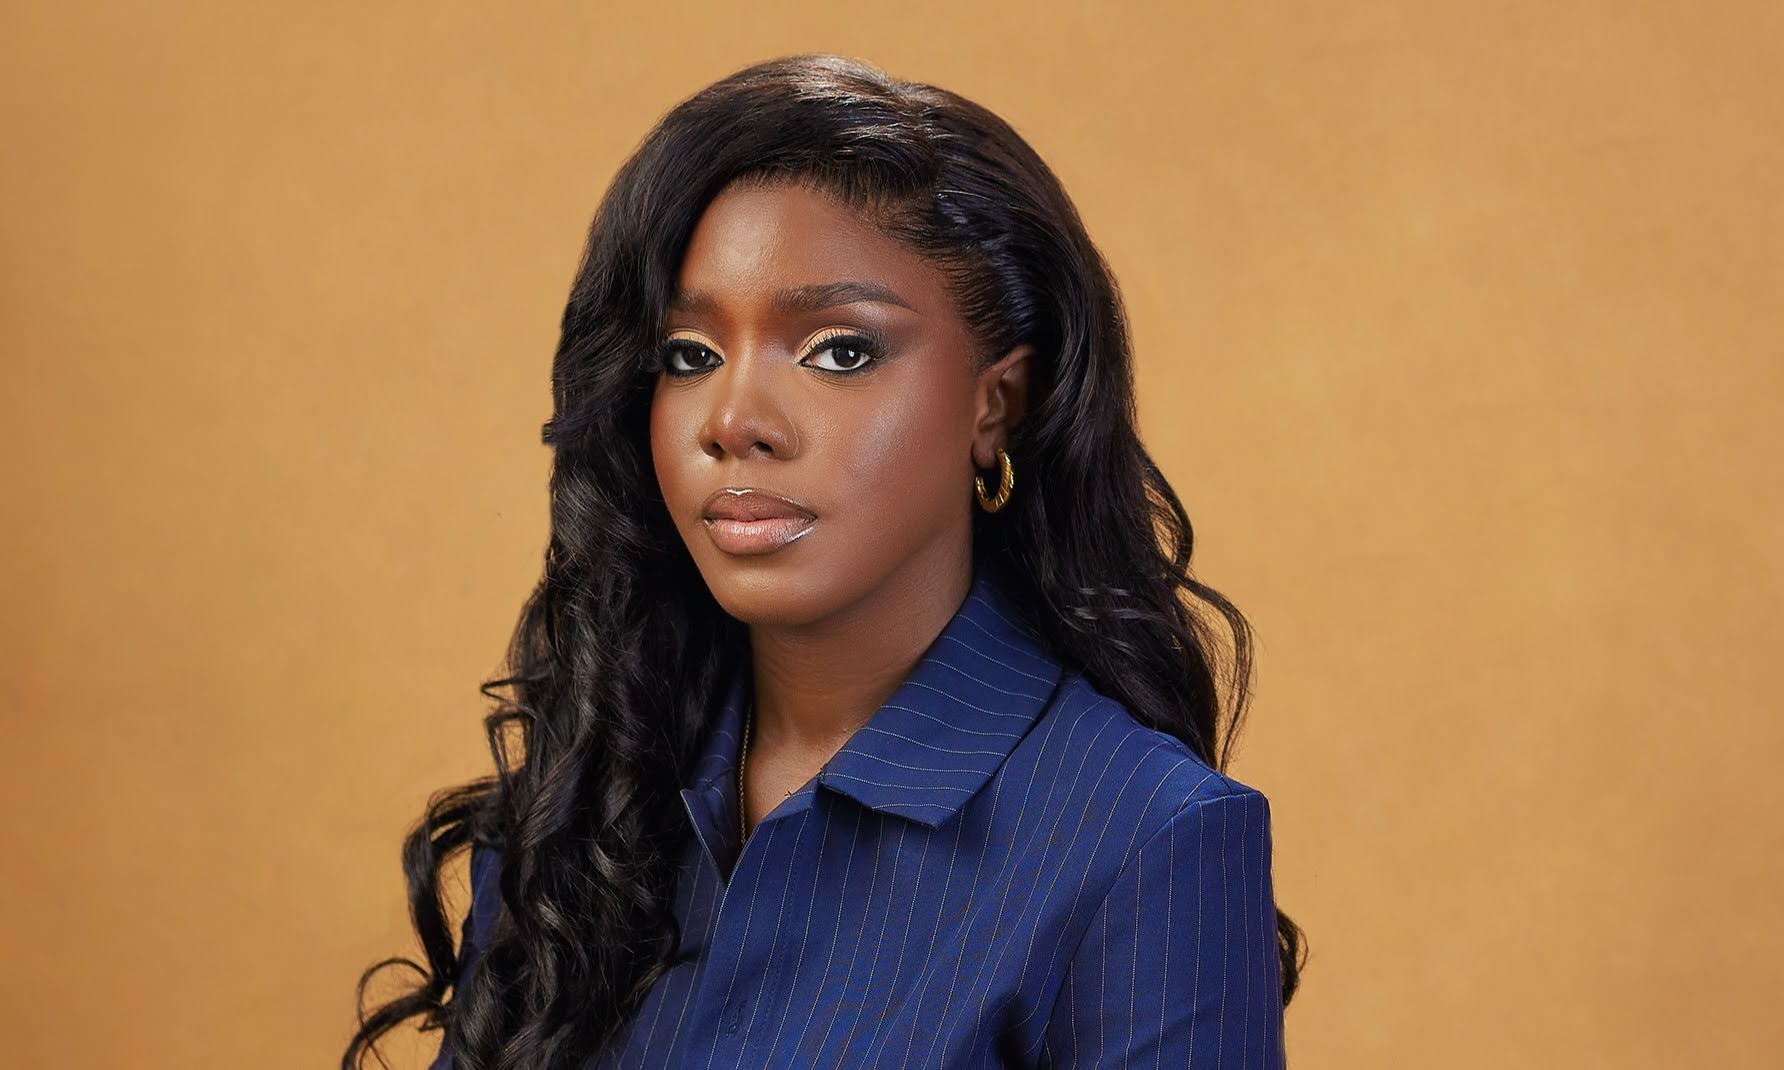
“Right now, the real frontier of big tech isn’t just the next AI model, it’s whether people can still trust these systems when they don’t understand them, and whether someone inside the room is willing to say no when that trust is at risk,” says Modupe Akintan, a Privacy and AI Engineer at a major technology company. It is the kind of remark that lands with unusual force at a time when trust has become a scarce resource in a digital economy that depends on ever-larger data flows and increasingly opaque automated decisions.
From a distance, Modupe’s résumé, including a first-class engineering degree in Nigeria, a security-focused master’s from Stanford, privacy engineering roles at Apple and one of the world’s largest technology companies, and a growing portfolio of policy and standards work, resembles the classic big-tech success story. Up close, the narrative is more complicated. Her chosen field, privacy engineering for AI systems, is less about validation than about interrogating the infrastructures and incentives that make data-hungry systems work.
Trust as a Design Constraint
Modupe’s field, privacy engineering for AI systems, designs the technical controls, risk assessments, and standards that protect personal data in AI systems, including autonomous AI agents. Its practical focus: turning legal and policy obligations into technical and organizational controls that real systems can live with. That means translating abstract requirements from data-protection law, AI regulations, and security standards into decisions about what data is collected, how long it is retained, who can access it, and which models are permitted to infer from it.
Industry roadmaps for 2026 emphasize the same convergence. Analysts argue that AI governance, privacy, and security must be treated as a single discipline if organizations hope to navigate tightening enforcement and increasingly complex threats. Pieces on “data privacy in 2025 and beyond” describe an evolving frontier shaped by evolving regulations, AI risks, and the growing importance of privacy-by-design approaches, warning that a single lapse can undermine confidence in entire classes of technology. For Modupe, these pressures are not reasons to slow innovation so much as arguments for treating trust as a design constraint from the outset.
From Nigerian Lecture Halls to Global Platforms
Her path began in far more traditional settings. In Nigeria, Modupe completed a Bachelor of Engineering in Computer Engineering at Afe Babalola University, graduating with first-class honors and recognition as Best Graduating Student in Computer Engineering for the 2020/2021 session, an achievement that drew local media attention at the time.
She went on to Stanford University, where she earned a master’s degree in computer science with a concentration in computer and network security. As a research assistant in the Stanford Empirical Security Research Lab, she compared the risk-rating methodologies of third-party risk management companies, examining how these vendors scored organizations’ security posture and how those scores shaped vendor relationships. The work highlighted how much institutional “trust” in complex ecosystems rests on models and metrics that outsiders find difficult to interrogate. “You realize that entire supply chains are leaning on scores they don’t fully understand,” she has said.
Frontiers of Big Tech, High-Level and High-Stakes
Today, Modupe works as a Privacy and AI Engineer inside one of the large cloud and AI platforms that are both the infrastructure of the digital economy and the subject of intensifying regulatory and public scrutiny.
At the same time, she contributes to the Cloud Security Alliance’s Data Privacy Engineering Working Group, which focuses on advancing practical approaches to protecting sensitive data through privacy-by-design, DataSecOps, and privacy-enhancing technologies. The group’s work reflects a broader shift in the technology industry toward embedding privacy protections directly into system architecture and data management practices, rather than treating compliance as an afterthought. For Modupe, these efforts reinforce the idea that trust in technology must be supported by safeguards that can be evaluated and demonstrated in practice. “Trust is becoming less about reassuring statements and more about whether your controls can withstand independent scrutiny,” she notes. “That’s where engineering and policy have to meet.”
Her interest in independent scrutiny extends to how AI developers document their models. In November 2025, she was one of five co-authors of a policy memo addressed to MIT and the Center for Democracy and Technology that proposed a standardized, machine-readable model card framework aligned with the EU AI Act’s technical documentation requirements, along with a weighted scoring method that counts safety-critical disclosures more heavily. The team evaluated the public documentation of 48 widely used AI models against the framework and built a working dashboard, the AI Transparency Atlas, to compare the results.
Trust, Inference, and the New Harms
One reason trust has become harder to define and easier to lose is the rise of inferred data. Strategic briefings on the 2025 privacy landscape describe a “governance nightmare” in which AI systems derive sensitive attributes from seemingly innocuous inputs, raising questions about consent, fairness, and the scope of regulation. These inferences can shape credit decisions, health recommendations, targeted advertising, and content moderation, often without users realizing what has been inferred or how it is being used.
For a privacy engineer like Modupe, this is where frontiers become visible. “When a system can infer more about you than you ever told it, the old consent model starts to break down,” she says. “Trust at that point depends on whether we’ve designed limits into the system, not just whether we asked you to click ‘I agree.'” Emerging AI regulations, including risk-based frameworks in Europe and principle-driven guidance elsewhere, increasingly demand impact assessments, documented safeguards, and demonstrable human oversight for high-risk use cases. Modupe’s work seeks to turn those expectations into operationalized outcomes for engineers and product teams.
Policy Fellowships and Contested Governance
As Director of Partnerships at the Paragon Policy Fellowship, she helped scope applied technology-policy projects and foster collaboration with government agencies, academic institutions, and industry partners.
Her contributions also include conference and standards work: serving on the program committee for the 41st IFIP SEC conference, peer reviewing for IEEE IATMSI 2025, and co-authoring and presenting a poster at IEEE Digital Platforms and Societal Harms (DPSH) 2024 on AI-driven misinformation risks in local government. When invited to judge early-stage projects at events like Vibe Demo Day, she says she asks a simple question: “What happens to the most vulnerable person who touches this system?” If the answer is unclear or unsatisfying, she considers the design incomplete.
A Critic’s Challenge: Trust or Theater?
Yet as trust language proliferates, some observers warn that “trust” risks becoming a form of theater. “We’re seeing a wave of trust-branded frameworks and privacy-preserving technologies marketed as differentiators, but far less willingness to walk away from intrusive business models,” says a policy analyst.
The analyst points to predictions that, despite low baseline trust in AI for high-risk scenarios, a growing share of consumers will still use generative tools for critical decisions in areas like finance and health. At the same time, privacy-preserving technologies are being promoted as ways to protect data while still extracting value from it. “These tools are important,” the analyst says. “But if they’re layered on top of systems that still incentivize maximal data capture and opaque inference, they may end up extending the life of practices that should be questioned more fundamentally.”
Redefining Trust From the Inside
Modupe is not blind to this tension. “Trust can absolutely become theater if it’s just a new vocabulary on top of the same decisions,” she says. “The work, at least the way I see it, is to change which decisions feel possible.” In practice, that can mean advocating for shorter retention windows, narrower data use, or more conservative model-deployment criteria, and accepting that some features may never ship if the risks cannot be responsibly managed.
She measures progress in small shifts: a system designed to avoid collecting sensitive attributes it does not need; a vendor contract that constrains secondary use; a governance process that forces discussion of societal harms before deployment. Those changes are rarely visible to users, but they shape the environment in which trust can either harden or evaporate. “The most meaningful trust work is often invisible,” she says. “A model we decide not to train, a pattern of inference we decide not to allow, those are the frontiers that matter.”
A Reflection on the Frontiers of Big Tech
When asked what it means to be described as a “rising privacy engineer” at the frontiers of big tech, Modupe pushes back on the heroic framing. “I don’t think of it as rising,” she says. “I think of it as joining a long line of people, lawyers, advocates, researchers, engineers, who have been arguing for a more honest relationship between technology and the people it governs.”
For her, redefining trust at those frontiers is less about personal trajectory than about collective responsibility. “If, ten years from now, people can rely on AI-driven systems without feeling constantly watched, profiled, or manipulated, it won’t be because trust suddenly ‘improved’ on its own,” she reflects. “It will be because enough of us, in enough rooms, decided that risk and privacy were not afterthoughts but the rules of the game, and refused to move the frontier forward unless trust came with it.”