
Securing the Storage Behind AI: Manita Ngarmpaiboonsombat’s Work with SPDM and TCG

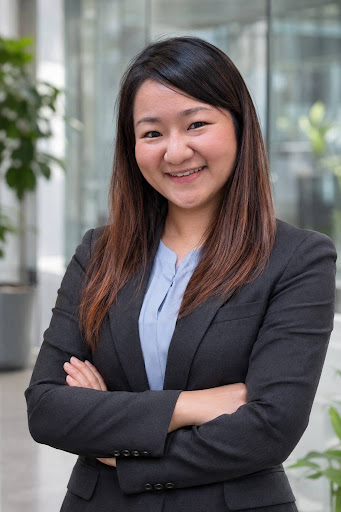
Device identity, firmware evidence and access controls are becoming part of the AI infrastructure conversation. Her focus is the validation software that helps engineers examine those protections.
An AI server can contain powerful processors and carefully protected applications while still depending on a basic question about its hardware: which components should the system trust? A second question follows close behind: who should be able to access the data stored inside it? Together, those questions put device authentication and storage security near the foundation of dependable computing.
For Manita Ngarmpaiboonsombat, a software developer at SANBlaze Technology, they are also part of an engineering assignment. Her current work includes Python-based validation software and security testing involving Security Protocol and Data Model, or SPDM, and Trusted Computing Group storage technologies. The objective is to help engineers evaluate whether security behavior meets its technical requirements before a product moves toward deployment.
It is a contribution made through executable checks: software that exercises a device, examines a response and makes an unexpected result easier to investigate. The practical value lies in turning a security feature described in a specification into behavior that can be examined repeatedly.
First, establish what the device can prove
SPDM provides a common language for security exchanges among components. DMTF, the organization behind the standard, describes capabilities including hardware identity authentication, firmware measurements and key exchange. Depending on the supported features and protocol bindings, those exchanges can help establish protected communications and provide evidence for a platform’s trust decisions.
A useful analogy is a controlled entrance that asks for identification and examines the evidence behind it. In a computer, that evidence can include a certificate chain and measurements related to firmware. A verifier evaluates the evidence against its policy. Receiving a response is only one step; the response must be interpreted correctly.
That is where validation becomes demanding. Devices may support different versions or combinations of capabilities. An unsupported request, an invalid certificate or an interrupted exchange can produce behavior that a simple demonstration never exercises. Test software helps engineers examine these conditions systematically and distinguish a genuine device problem from an unsuitable test setup.
Ngarmpaiboonsombat’s focus is on the validation side of this process. Python automation provides a way to organize protocol interactions, repeat a sequence and retain results for review. The engineering challenge includes making a result traceable to the request, the conditions and the requirement being evaluated. A security claim becomes more useful when another engineer can examine how it was tested.
A technology already visible in the AI hardware ecosystem
SPDM has concrete implementations in the wider industry. NVIDIA’s Corelib documentation describes a library that collects GPU attestation evidence through SPDM interfaces, including firmware measurements and certificate information. Its documented support includes Blackwell GPUs. This places the protocol within an identifiable AI hardware environment, rather than leaving it as a theoretical security proposal.
NVIDIA’s implementation and SANBlaze’s validation tools occupy different parts of that ecosystem. One illustrates the collection of device evidence; the other provides tools for evaluating protocol behavior. The connection is the growing need to understand whether the security exchanges underneath an AI platform work as intended.
SANBlaze’s own SPDM product page describes validation for operations including protocol negotiation, certificate handling, device authentication and secure-session establishment, alongside automated regression execution. These public capabilities show the kind of engineering environment in which Ngarmpaiboonsombat’s security-testing work sits.
Then, examine protection of the stored data
TCG storage security addresses a related set of questions about protection and control within a storage device. The Trusted Computing Group describes an architecture covering self-encrypting drive behavior, authorization, storage locking and security subsystem classes such as Opal and Enterprise. These mechanisms can help control access to data at rest and manage security functions on the device.
The distinction matters. SPDM supports component authentication, evidence exchange and protected sessions. Storage security mechanisms such as TCG Opal concern functions including authorization and locking of stored data. An organization can need both, and the behavior of each must be evaluated on its own terms.
For testing, a meaningful question might be whether an authorized operation succeeds in the expected state and whether an unauthorized operation is rejected. Another could involve what happens when a security configuration changes or a device returns to a defined state. These are examples of validation questions; the answer depends on the applicable specification and the device’s supported capabilities.
Her work with these technologies brings attention to the implementation detail behind a broad promise such as secure storage. A feature needs an operational definition. A test needs an expected outcome. A result needs enough context to support investigation. Building software around that chain is a substantive engineering responsibility.
The impact is in the decisions engineers can make
The immediate users of validation software are often development, quality assurance and qualification teams. They need to determine whether a device behaves correctly, whether a change introduces a regression and what evidence supports a release decision. Automated testing can make it practical to revisit those questions as firmware and configurations evolve.
For the organizations that later rely on those devices, the stakes include the protection of stored information, predictable handling of access and confidence in the components supporting a service. Well-designed validation helps expose mismatches between an advertised capability and its observed implementation. That contribution supports risk assessment before a system becomes harder to change.
Ngarmpaiboonsombat’s role reflects an increasingly important part of infrastructure engineering: examining the security behavior that other layers of a system assume they can trust. The work gives practical substance to a familiar ambition for AI building systems people can rely on by starting with the devices, exchanges and storage controls underneath it.




Comment