
Built for the CISO: How ‘SecuraTrack’ Turns Compliance Into Real Security

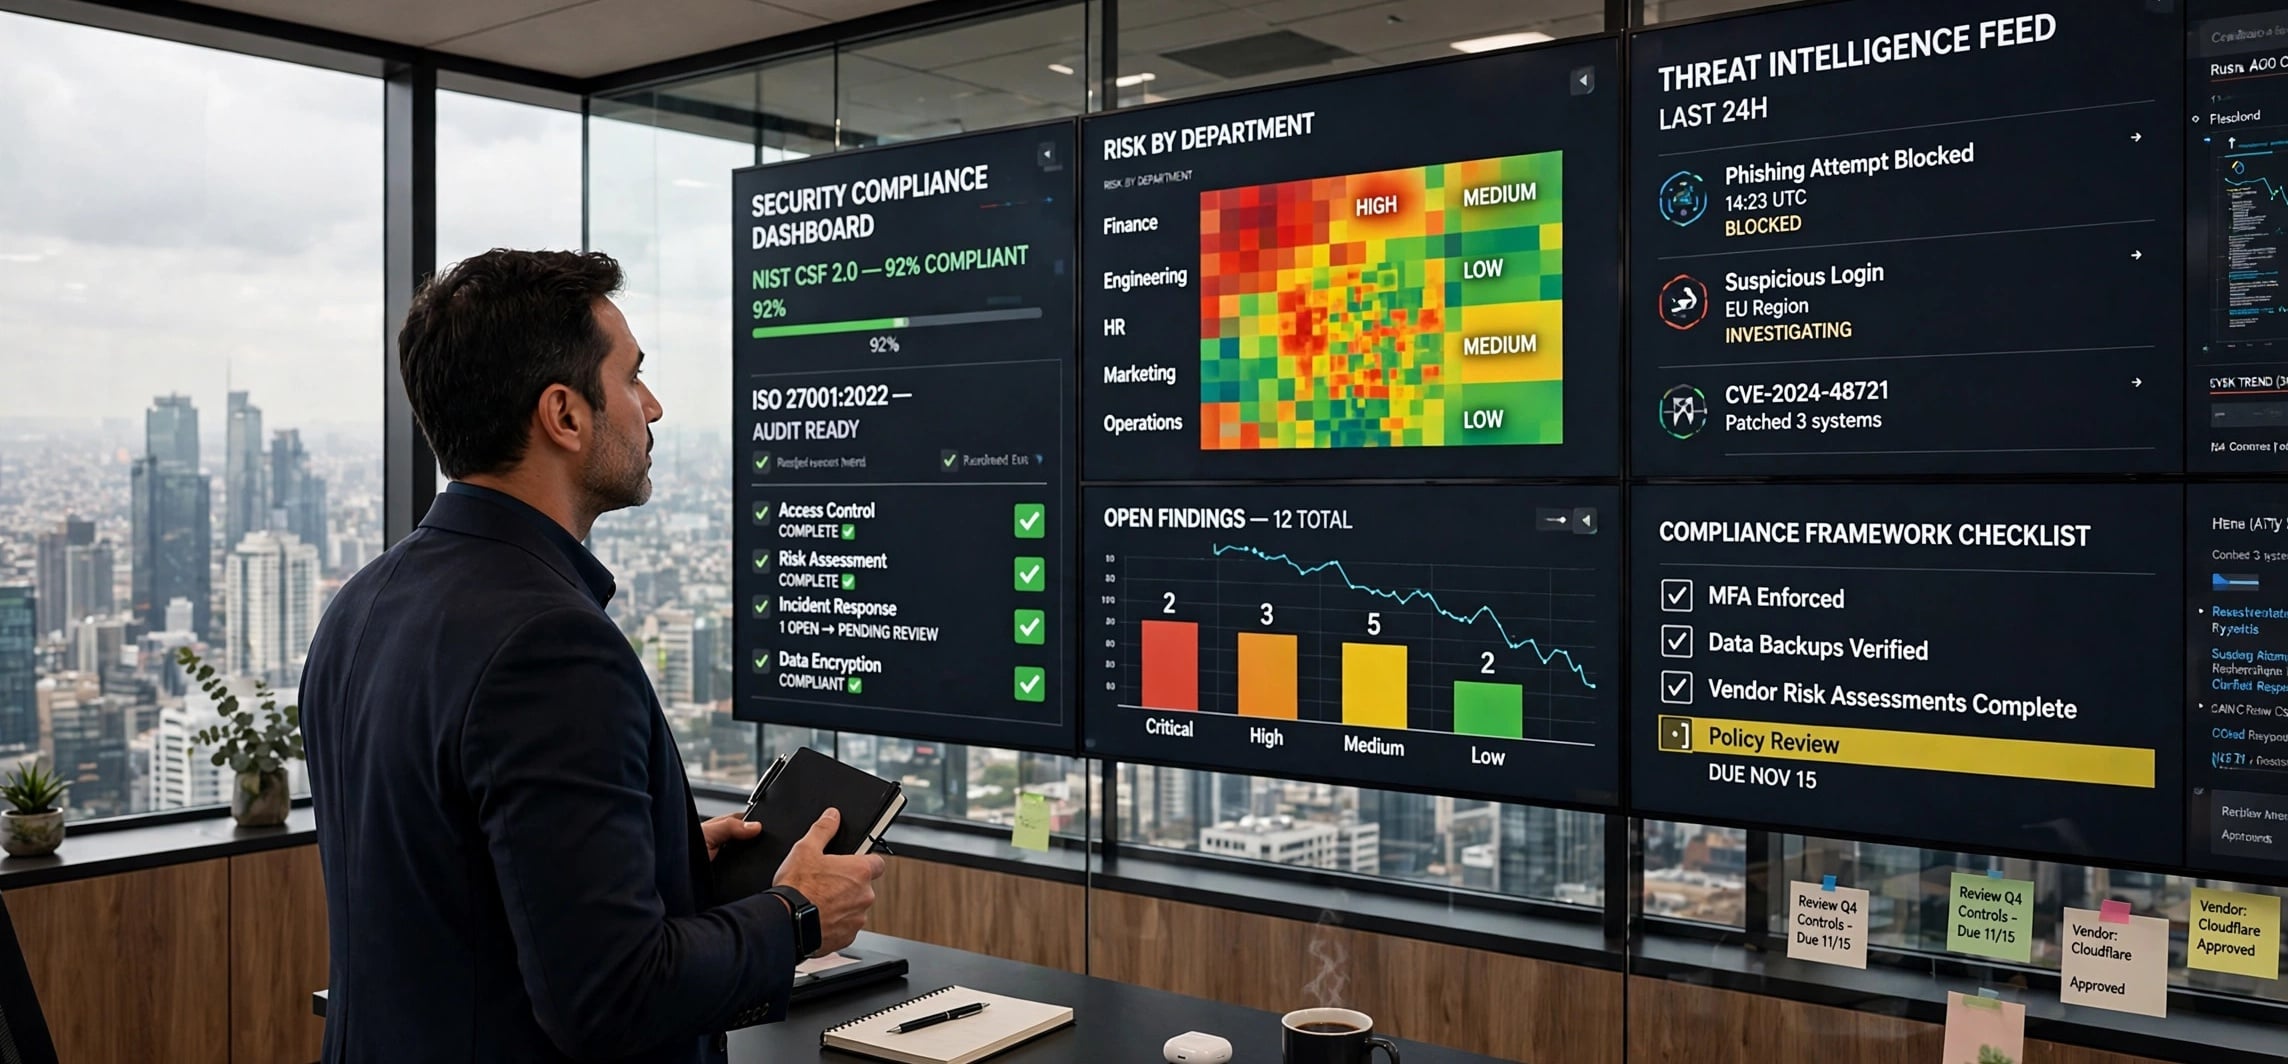
All-in-one tools and AI models promise to address challenges across a broad spectrum of business operations. However, a broad approach can also raise questions about how effectively these solutions address specific individual or business needs.
SecuraTrack offers a different perspective. Rather than attempting to cater to multiple business operations and departments, they offer a platform that is exclusively focused on catering to the needs of Chief Information Security Officers (CISOs). They offer to help CISOs with compliance, risk management, security risks, and the organization’s overall security posture.
One of the defining pain points of many CISOs and security leaders of mid-size companies was investing more time and effort into tools and paperwork than in managing security. SecuraTrack curbs this by offering a solution that meets security and AI regulations at once with less effort, lower cost, and full control over data.
The Founder’s Story: The Birth of SecuraTrack
SecuraTrack was brought to life by Nikolcho Panov’s vision, who spent more than two decades working across information security, cybersecurity consulting, and risk management. Having worked with top organizations, he had first-hand experience with security leaders across different industries encountering similar challenges despite operating in different environments.
Nikolcho Panov
Managing compliance requirements, overseeing security controls, and maintaining an organization’s security posture as a vCISO and GRC advisor often required considerable time and coordination. These recurring challenges became the foundation for SecuraTrack’s development.
Nikolcho’s educational background, including a Master’s in Information Security Management from Politecnico di Milano and an MBA from Hult International Business School, contributed to his understanding of both technical security requirements and organizational management. He is also currently undertaking MIT’s CTO Program, through which he and his co-founder, Eugene, who serves as the company’s CTO, developed the idea into a product.
Nikolcho has defined the work of SecuraTrack through three exemplary features:
1.) Bring Your Own Large Language Model (LLM)
One of the challenges the founder of SecuraTrack, Nikolcho Panov, faced when entering this market was keeping up with AI. After speaking with CISOs, he found they wanted AI’s speed but on a model they controlled.
SecuraTrack, hence, initiated a process that provided customers a chance to bring their own LLMs. It helps them choose a model that fits their policies and goals, and the platform is designed to work with it.
2.) Expert Consultancy
SecuraTrack demonstrates a unique approach to assist its customers. They do not just offer the platform; they offer a journey. They ensure every security leader’s and CISO’s requirements and goals are met and offer setup, support, and expert consultancy.
What this does is provide CISOs with an opportunity to customize the requirements and the features offered by SecuraTrack to their own LLM system, security posture, and data control.
3.) Cross-reference Across Frameworks
CISOs do not use one specific framework but rather utilize the features of multiple ones. With 45+ frameworks at their disposal, CISOs can use SecuraTrack to implement one control for every other standard that requires the same control.
That is to say that SOC 2, ISO/IEC 27001:2022, HIPAA, NIS2, NIST CSF 2.0, and the 40 other frameworks can follow the same command across the board.
What does SecuraTrack Offer?
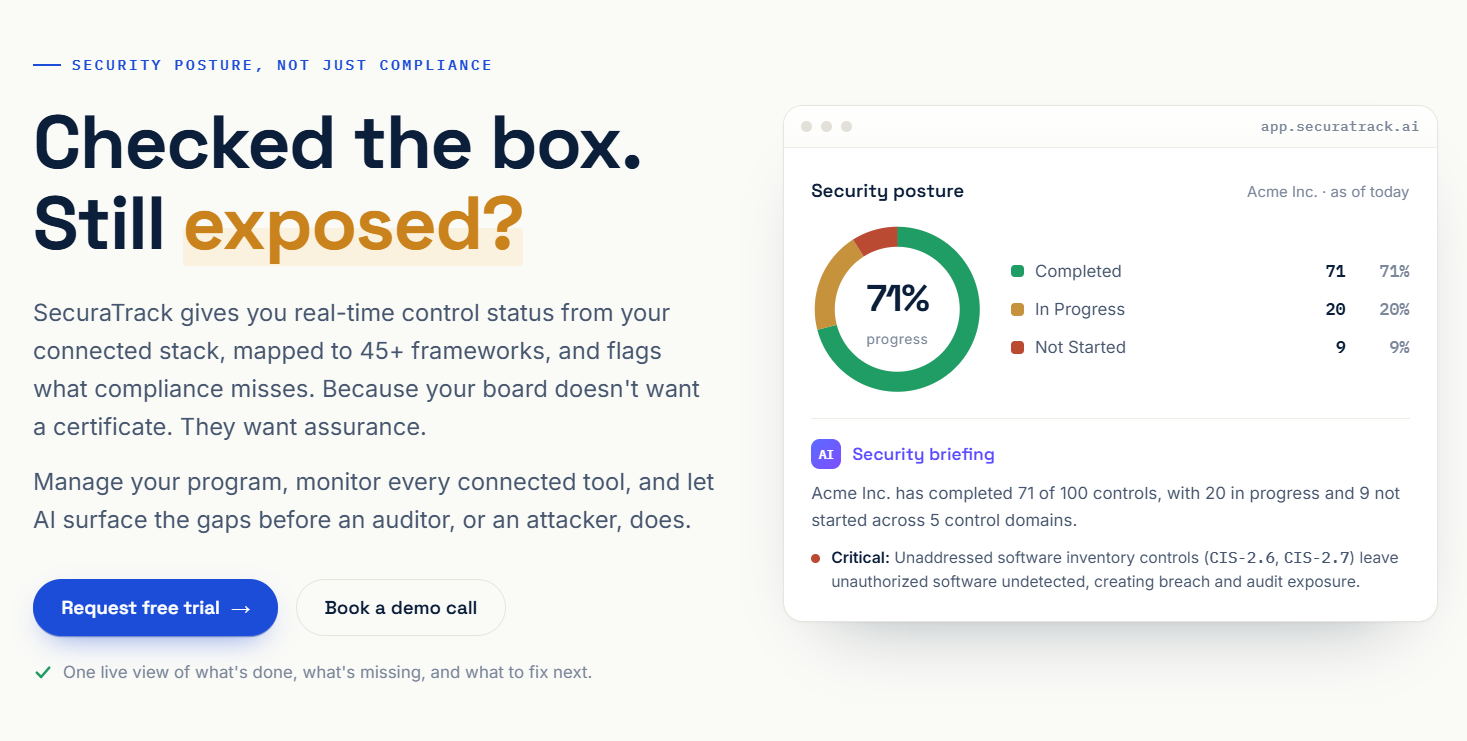
SecuraTrack’s platforms also offer an AI-powered posture dashboard that helps with governance, risk management, and compliance. They have also offered a risk tracking and assessment view that records, classifies, and tracks risks before they become incidents. Simultaneously, they offer continuous automated audit readiness across multiple frameworks.
This exposure on their platform gives stakeholders a holistic view without putting too much effort into paperwork and switching between different tools. Moreover, it helps to overcome gaps before they make an unexpected appearance, be ready for an audit at any time of the year, and offer board-level clarity.
Addressing the Growing Demands of AI Governance
As AI becomes increasingly integrated into business operations, security leaders must consider the benefits of these technologies and the risks associated with their implementation. Protecting sensitive information, maintaining oversight of AI systems, and understanding evolving regulatory requirements have become important considerations for organizations adopting AI.
Frameworks such as the NIST AI Risk Management Framework and regulations such as the EU AI Act reflect the growing emphasis on responsible AI governance. For CISOs, these developments add another layer of responsibility to existing cybersecurity and compliance obligations.
SecuraTrack’s approach to customer-controlled AI addresses one of the central concerns surrounding the adoption of AI in security operations: maintaining control over sensitive data while benefiting from AI capabilities. By allowing customers to bring their own LLMs, the platform is designed to accommodate their chosen models and organizational policies.
This approach reflects SecuraTrack’s broader objective of making security management more manageable without overlooking the importance of data control and governance.
Supporting CISOs Beyond Compliance
For many organizations, managing compliance involves more than preparing for an annual audit. Security controls, business operations, and regulatory expectations can change over time, requiring organizations to continually review their risk exposure and compliance status.
SecuraTrack seeks to support this ongoing process through its security posture dashboard, risk assessment and tracking capabilities, and multi-framework compliance features. By bringing these functions together, the platform aims to give security leaders and other stakeholders a clearer view of their organization’s security position and the areas requiring attention.
Its cross-framework approach also addresses the repetitive work associated with maintaining compliance across multiple standards. Instead of treating every framework as an entirely separate process, SecuraTrack maps overlapping controls to help organizations manage common requirements more efficiently.
A Future Focused on Giving CISOs Back Control
SecuraTrack’s immediate goal is to establish a base of satisfied customers by demonstrating practical value to the security leaders it serves. Its longer-term vision is to become a platform that mid-sized companies can rely on to understand their security posture and manage the compliance standards applicable to their organizations.
At the heart of this vision is a simple principle: compliance should support security rather than become a substitute for it. While regulatory requirements remain essential, organizations must also understand whether their security controls are effective and whether emerging risks are being addressed.
By combining a CISO-focused platform, customer-controlled AI, cross-framework compliance, and expert consultancy, SecuraTrack aims to help security leaders move away from fragmented tools and repetitive paperwork. Its objective is to give CISOs greater visibility and control over their responsibilities, allowing them to devote more attention to the security challenges that matter most.




Comment