
Zero Trust Before Launch: How One Lead Engineer Secures a Platform Used by 150,000 Advisors

Muhammad Zeeshan treats security as a layer of the platform and not as a step before release.
A travel booking platform holds names, passport details, itineraries and card data in one place. Every one of those records is a target, which means the way a platform is built matters more than any single security tool added to it.
Muhammad Zeeshan is the engineer who owns how that data is protected on a platform that sells through more than 150,000 independent advisors in the United States, the United Kingdom and Ireland. He is a Technical Lead and AI and Enterprise Software Engineer with Media Mind Management LLC, a Florida company, and he works from Gujranwala, Pakistan.
His approach starts with a simple rule: trust is not permanent. In a Zero Trust model, no user, device or request is trusted just because it is already inside the system. Access is checked each time. On the platform he works on, access follows a Zero Trust model built on AWS IAM.
That decision was made early. When the platform’s booking engine was rebuilt starting in March 2019, security was written into the requirements next to features. The old system lacked fraud checks, 3D Secure transactions and compliance measures. The rebuild brought in PCI DSS compliance, accessibility to ADA standards and penetration testing obligations.
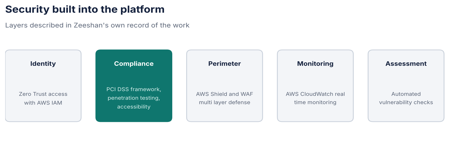
His description of the infrastructure has five parts. Access follows the Zero Trust model. The PCI DSS framework governs how payment data is handled. AWS Shield and a web application firewall defend the perimeter in layers. AWS CloudWatch watches the systems in real time. Automated checks look for vulnerabilities before an attacker does.
The order matters. Security added after release has to work around decisions that were already made. Security written into the requirements shapes those decisions, and it is far easier to keep consistent as the platform grows.
Zeeshan also carries the operating work. He controlled server deployment for the platform and set the cybersecurity rules for it, and his remit includes disaster recovery and card industry compliance. He has also investigated escalated insider threat incidents, which is a reminder that the threat is not always outside the walls.
The goal is to protect sensitive personal data while keeping the experience smooth for advisors who book all day. Payments show how the two fit together. Cleared payments use 3D Secure 2 by default, and a written layer of rules sits between a vendor’s fraud score and the payment authorization, so each decision can be traced to the rule that made it.
He has written about this kind of design as well. His 2026 paper in the Journal of Intelligent Decision Making and Information Science, “Trustworthy AI for Financial Fraud Prevention: Explainable Risk, Privacy and Secure Decision Architecture”, proposes keeping risk estimation separate from the policy a platform owns. It also inventories personal data field by field and removes it at the trust boundary, and it scopes the cardholder data environment so an external scorer falls outside PCI DSS assessment.
His credentials back this up. He holds the AWS Certified Cloud Practitioner, AI Practitioner and Developer Associate certifications. He is an IEEE Senior Member, he has completed 44 peer reviews across eight publications from IEEE, Springer Nature, PLOS ONE and Elsevier, and he has reviewed conference papers on fraud detection, digital payments and secure banking architecture.
The next stage of his work is about automation. He describes his current direction as secure AI automation: systems that remove manual, error prone work while keeping data protected. An itinerary builder is now in development that creates trips from a customer’s preferences, interests and budget, and the same discipline applies to it as to the booking engine: decide how data is protected before the feature ships.
The blueprint in his paper is vendor neutral, which means other teams can adopt the design without adopting any one supplier. He is also due to deliver a keynote on November 21 and 22 at the International Conference on Smart Computing and Information Systems at the University of Canberra.
The larger point is one that applies well beyond travel. The question for any platform is no longer whether to strengthen security, but whether it has been built into the architecture from the start, and whether it can be shown to work. Zero Trust is one part of that answer.




Comment